September 13, 2026 Post by : Editorial Security Leadership
What Threat Intelligence Actually Means for a Small Security Team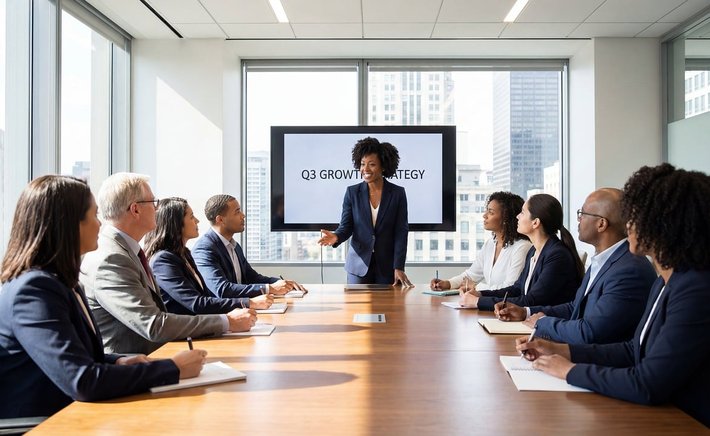
Ask a security leader what frustrates them most and a common answer comes up: the board does not get it. Ask a board member what frustrates them most and you will often hear the opposite: security keeps telling us we are doomed without telling us what to do about it. Both are usually right, and the gap between them is mostly a communication problem.
The issue is not intelligence. Most executives understand risk. They manage it every day in the form of market exposure, hiring decisions, and capital allocation. What they do not have is a mental model for cyber risk that connects to the way they already think. When security briefings arrive as a list of vulnerabilities with CVSS scores, the audience checks out. When they arrive as a story about a business process that could stop working, the audience leans in.
Translate, Do Not Simplify
There is a difference between dumbing something down and translating it. Dumbing down means removing detail until the message is useless. Translating means keeping the substance and changing the frame. A vulnerability that allows remote code execution on a public-facing server is not interesting to a CFO. The same vulnerability described as "an attacker could take control of the system that processes customer payments, and we would not know for days" is interesting to almost anyone.
Executives also respond well to comparisons. Not benchmarks pulled from a vendor report, but honest internal comparisons. How does this risk compare to the risk we accepted last quarter when we delayed the firewall refresh? How does it compare to the risk of pausing the new product launch to fix it? Framing choices as trade-offs, rather than as a list of demands, changes the conversation.
It helps to bring a small number of decisions, not a large number of updates. Boards are decision-making bodies. If a briefing contains no decisions, it is really just a status report, and those can be sent by email. The most effective security briefings I have seen contain three things: what changed since last time, what we recommend, and what we need from you.
Building Trust Before You Need It
The worst time to build a relationship with the board is during an incident. The best time is in the quiet months when nothing is on fire. That means showing up regularly, being honest about what you do not know, and following through on what you said you would do. Consistency builds credibility faster than any single presentation.
It also means owning the failures. If a project slipped, say so. If a control did not work as expected, say so. Executives have seen enough vendors and consultants to recognize spin when they hear it. The security leaders who last are the ones who treat the board as a long-term relationship rather than a quarterly performance.
None of this makes the technical work easier. But it changes the environment in which that work happens. A security program with executive support can hire, can invest, and can say no to projects that would create unacceptable risk. A program without that support fights for scraps. The difference is rarely technical. It is almost always about whether the people holding the budget understand what they are buying.
Author
22 feb,2025
This incident opened my eyes to the value of Insurance in general, so I decided to examine my personal and business insurance.
Comment (3)
The payments are made directly from one person to another without passing through a central bank or clearing house.
22 feb,2025
ReplyWhat Threat Intelligence Actually Means for a Small Security Team
23 feb,2025
ReplyPhishing Kits Have Gotten Boring, and That Is the Problem
23 feb,2025
Reply